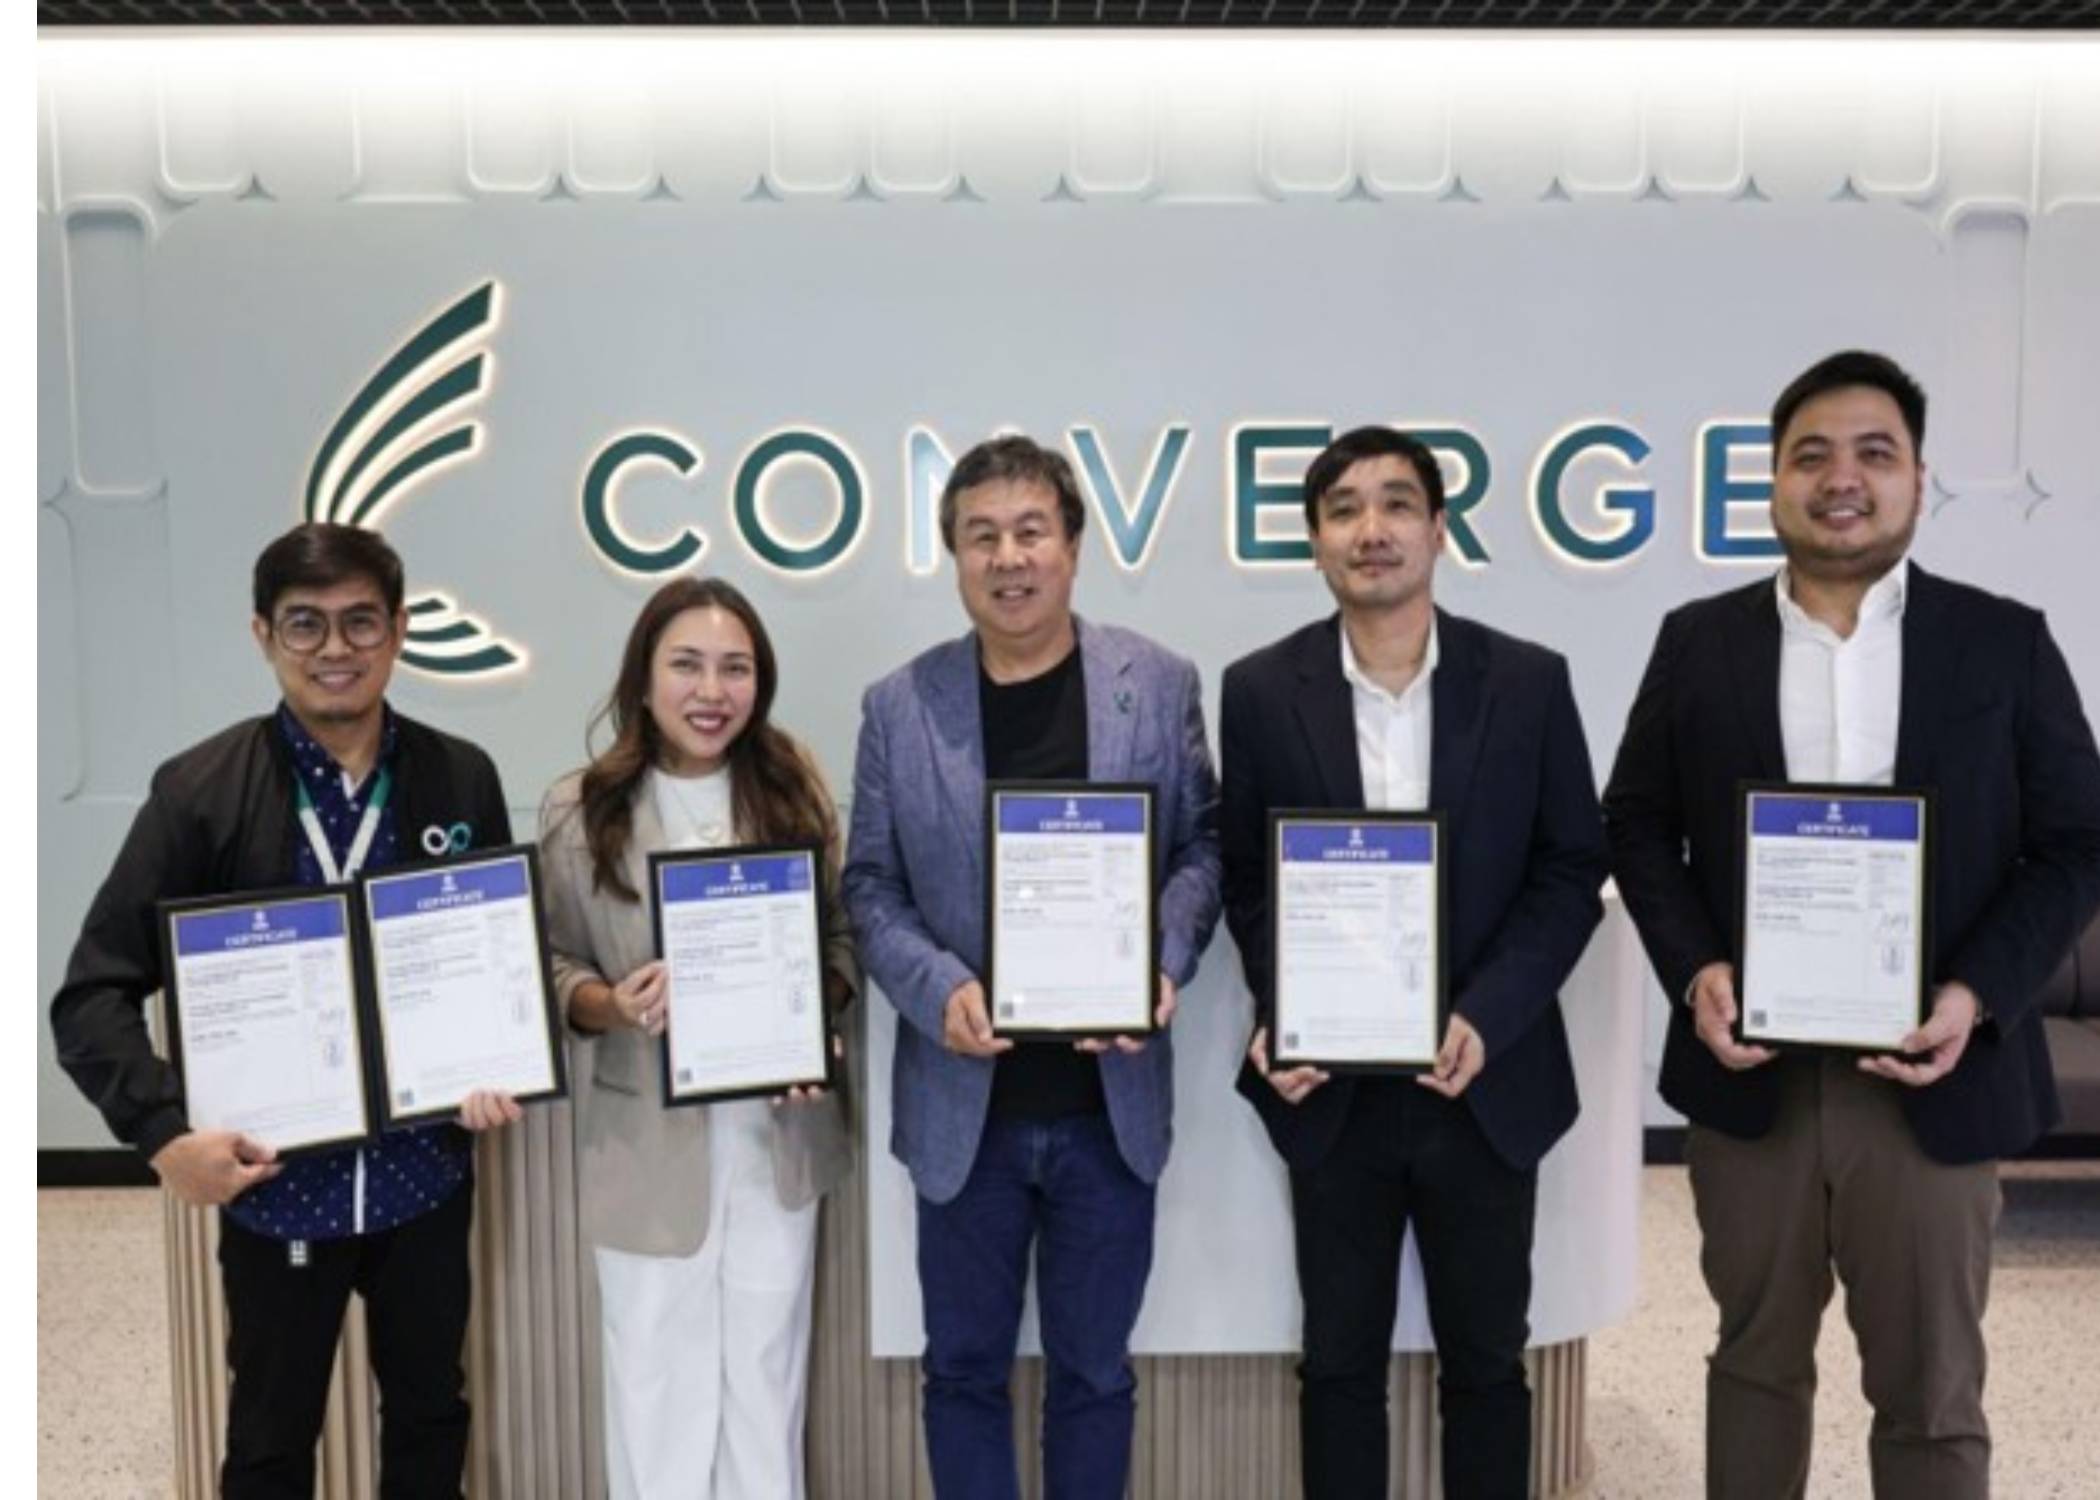
Leading fiber broadband and technology provider Converge ICT Solutions Inc. has earned the globally recognized standard for Information Security Management Systems (ISMS) – ISO/IEC 27001:2022 certification – reinforcing its commitment to protecting information, upholding robust cybersecurity, and building trust with its customers and stakeholders.
The certification represents a significant operational and regulatory milestone in the company’s effort to establish rigorous information security practices across its operations.
“We recognize that protecting information is fundamental to our role as a broadband provider, given the vast amount of customer data that we handle. We understand the responsibility that comes with serving millions of customers and safeguarding the information they entrust to us. This drives our adoption of internationally recognized standards across our operations, demonstrating our commitment to continuously enhance the systems running our business,” said Converge Corporate Compliance, Data Protection, and Corporate Sustainability Officer Atty. Laurice Esteban-Tuason.
The accreditation was awarded by Bureau Veritas, a globally recognized leader in testing, inspection, and certification services.
The ISO/IEC 27001 standard provides companies with guidance for establishing, implementing, maintaining, and continually improving an information security management system. It validates a company’s ability to support customers in an environment where security, privacy, resilience, and trust are increasingly critical.
Receiving the accreditation means Converge is equipped to mitigate modern cyber threats, proving its ability to serve industries with strict data compliance needs, such as business process outsourcing (BPO) firms and financial institutions.
Converge is advancing its transformation from a telco firm into a technology company, broadening its portfolio beyond connectivity to address a wider range of enterprise needs. The company is also strengthening its B2B business by expanding its reach among larger enterprises and organizations with increasingly complex digital requirements.
“As the digital landscape evolves, our commitment is to remain an organization fully equipped to navigate emerging risks and challenges. We will continue to elevate our security practices to ensure that our data is protected against evolving cyber threats,” said Converge SVP and Head of Corporate Information Security Office Andrew Malijan.
Adopting the ISO/IEC 27001:2022 standard exemplifies the broader commitment of Converge to operational excellence and technology leadership, reinforcing its position as a leading provider of digital connectivity and services in the country.